Search results for tag #homelab
ZimaBoard 2 review: x86 SBC with PCIe and dual SATA, benched against Raspberry Pi 5 and Orange Pi 5 Plus. Thermals, throttling, and where the hype dies. https://www.valtersit.com/guides/zima/zimaboard-2-review/ #homelab #sbc #proxmox

<StarCraft 2 voice> Hell, it's about time.
$ sudo do-release-upgrade
Checking for a new Ubuntu release
= Welcome to Ubuntu 26.04 LTS 'Resolute Raccoon' =
So I spent a number of hours last night trying to figure out why my beautifully crafted firewall rules in pfSense suddenly stopped blocking outbound traffic when my VPN gateway was down.
It turns out newer versions of pfSense changed the firewall rule behaviour so that if you have a rule such as "if traffic source is (LAN subnet) and destination is not(LAN subnet), use VPN gateway" to force traffic over the VPN, then when the VPN gateway is down it *silently* changes the "use VPN gateway" to "use default gateway", and makes you start leaking encrypted traffic. It's so upsettingly shit 😅
Anyway, I found the relevant setting in "System -> Advanced -> Miscellaneous" and now all my firewall rules don't suddenly drinking silly-juice whenever the VPN blips.

Alt...
A screenshot of the pfSense web UI showing the "Gateway Monitoring" options. One option is highlighted in red:
"Skip rules when gateway is down
Do not create rules when gateway is down By default, when a rule has a gateway specified and this gateway is down, the rule is created omitting the gateway. This option overrides that behavior by omitting the entire rule instead. "
This is disabled by default and causes the aforementioned absolutely cursed behaviour

Do you run #IPS (Intrusion Prevention System) and/or #IDS (Intrusion Detection System) features on your home #Network?
Feel free to elaborate on why or why not, I like to hear what real users do and think vs just what tech news articles have to say about these things.
| yes: | 0 |
| no: | 0 |
| other/explain: | 0 |
Closes in 5:08:01:00

Well that's one way to fill up your server rack. (Not fully off-grid yet, but hopefully soon.) #homelab

Alt...
A server rack with two LFP battery packs installed.

pvetui v1.4.4 is out!
Highlights:
• CLI now accepts guest names, TUI adds quit confirm & startup options, version tag typo fi...
Full notes: https://github.com/devnullvoid/pvetui/releases/tag/v1.4.4 #proxmox #linux #homelab

This is not a good resource for me.. there goes my weekend out of the window!
#selfhosting #homelab #linux #hosting #proxmox #provisioning
Finally stopped YOLO-ing my AI coding agents. 😆 Moved them into agent-sandbox pods under gVisor, and built a Headlamp plugin so I can poke at them from my phone. Wrote up the setup and the quirks that bit me:
https://jj.macalinao.org/moving-my-coding-agents-into-kubernetes/

Well then…
After three years at Tailscale, today I’m starting a new chapter at Unraid as Head of Product Marketing.
I’m proud of what we built at #tailscale and enormously grateful to the people I worked with, and to everyone who watched the videos. 1600 subs to 78k, 10m views, and over 150 videos. Not too shabby.
Now I get to spend more time furthering the self-hosting mission I care so much about. I’ll be doing product work, community, technical education and, yes, plenty of video. There’s some really good stuff being worked on, and Unraid 8 will be a huge release.
So @computer.bringyourown.computer@bsky.brid.gy didn't manage to wipe over the network, but back office + Mac dock with Ethernet got it up and running. TinyHome lives! On to a 2-node proxmox cluster, just because!
Alt...
An extremely messy desk - a Lenovo m900 tiny is plugged into an Ethernet jack on a Mac dock into a Macbook Air and it only has displayport into a big monitor behind it. There is detritus on the desktop.

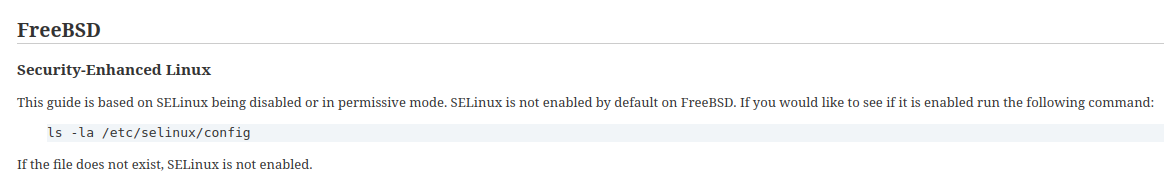
Well that's interesting. Nagios' own #documentation for installing on #FreeBSD includes steps for #SELinux. 🤔
#sysadmin #homelab #tech #monitoring #funny #hmmm
Alt...
Steps for installing Nagios4 on FreeBSD also includes info on SELinux. Why?!?!
This morning after reading the #FreeBSD Handbook chapter on Jails I had a massive realization. Look, I've dabbled in jails over the years but it was really just scratching the surface. But after reading about VNET Jails....this is some deep, mind-expanding awesomeness. One can run entire workloads completely segregated by a complex virtual network with VLAN tagging, independent network stacks, routing, and switching internally on one OS on a single kernel. Not that I have a use for it (yet) but this is truly exponentially mind blowing.
It's clear FreeBSD is *the* infrastructure operating system.
#BSD #RunBSD #tech #homelab #vnet #Jails #FreeBSDJails #infrastructure #networking
TIL: https://community-scripts.org now supports both #Proxmox and #Incus!
How feasible is it to migrate containers between Proxmox and Incus? Asking for myself 🤣
Read a bit o about #Incus, an alternative to #Proxmox for running VMs and containers on your own cluster.
Tl;Dr: Incus is more CLI -> REST API with optional, maybe less complete web UIs. Proxmox has excellent capable web UI, plus CLI if you want that.
Something I like very much are #Proxmox helpers which will set any number of services up for you, creating and configuring the container and installing the service.
Incus expects you to automate more things yourself.
Your ZimaBoard's 32GB eMMC will quietly kill your Proxmox root before the N3450 ever does. Real thermals, PCIe expansion and WireGuard tuning on the Celeron. https://www.valtersit.com/guides/zima/zimaboard-as-a-home-server-n3450-pushed-to-its-limits/ #homelab #zimaboard #proxmox
#HomeLab
#SelfHost
#Networking
Hive mind, do any of your run an #OpenBSD #FireWall on a mini PC? I ran one in the past on a multi-nic midtower. I may need to build a firewall again.
I know the BSD support is *very* hit or miss for hardware specifics. I was curious if any of you had luck so I don't have to find a used PC and put two supported NICs in it.