Search results for tag #security

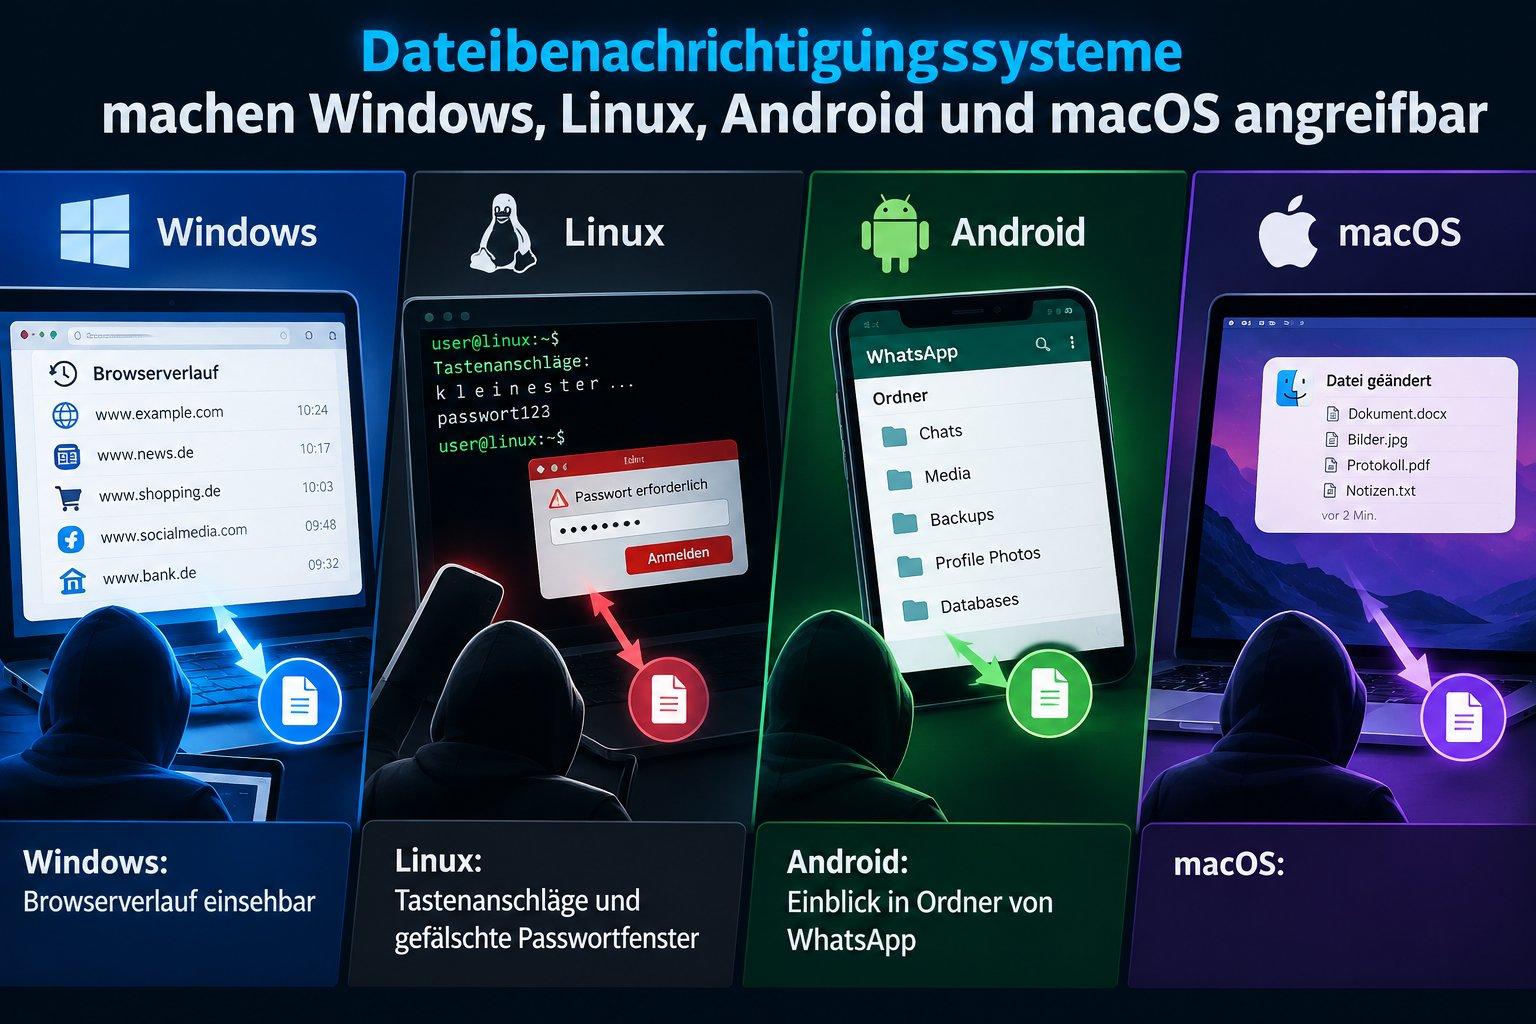
Dateibenachrichtigungen: Forschende der TU Graz finden Schwachstellen in Windows, Linux, Android und macOS
Zugriff über lesbare Ordner
Windows: Browserverlauf einsehbar
Linux: Tastenanschläge und gefälschte Passwortfenster
Android: Einblick in Ordner von WhatsApp
#cybersecurity #security #linux
Passend zum DiDay möchte ich euch meinen Privacy Guide ans Herz legen. Mit den vorgestellten Einstellungen für den Firefox-Browser erhöht ihr die Sicherheit und stärkt eure Privatsphäre auf einfache Weise: https://gnulinux.ch/privacy-guide
Und wenn ihr mehr davon wollt, findet ihr am Ende des Artikels einen Link über den ihr mich unterstützen könnt 

For some decades experts on the UK's food system have warned about its vulnerability to shocks (political & environmental); now this warning has been re-emphasised with (another) open letter to the Govt. arguing for better preparation by the state & more support for local & individual efforts to build better food resilience in the face of likely future threats.
Of course, you can store food yourself, but as a country we really need to do more.
#food #security #politics
https://www.theguardian.com/business/2026/oct/05/british-government-food-national-security-crisis-shortages
I thought I was long past blase about this kind of silliness, but then this afternoon
Oct 4 16:03:56 netflag sshd-session[9157]: Failed password for invalid user sickbeard-custom from 109.160.32.37 port 59414 ssh2
But hey, welcome to the spamtraps!
#ssh #sshgropers #passwordgropers #passwordguessers #spamtraps #cybercrime #cyber #security #cybersecurity

#MedicalRecords giant Epic pauses product development on #MyChart to fix #security bugs that risk patients' data
Judy Faulkner, the founder and chief executive of Epic, told Modern Healthcare last month that the pause would likely last six weeks while work continues on “safeguarding” the company’s products, after a deployment of #Anthropic’s frontier #cybersecurity model #Mythos unearthed security flaws that could allow access to patients’ data.
https://techcrunch.com/2026/10/02/medical-records-giant-epic-pauses-product-development-to-fix-security-bugs-that-risk-patients-data/
https://archive.ph/iwy4m
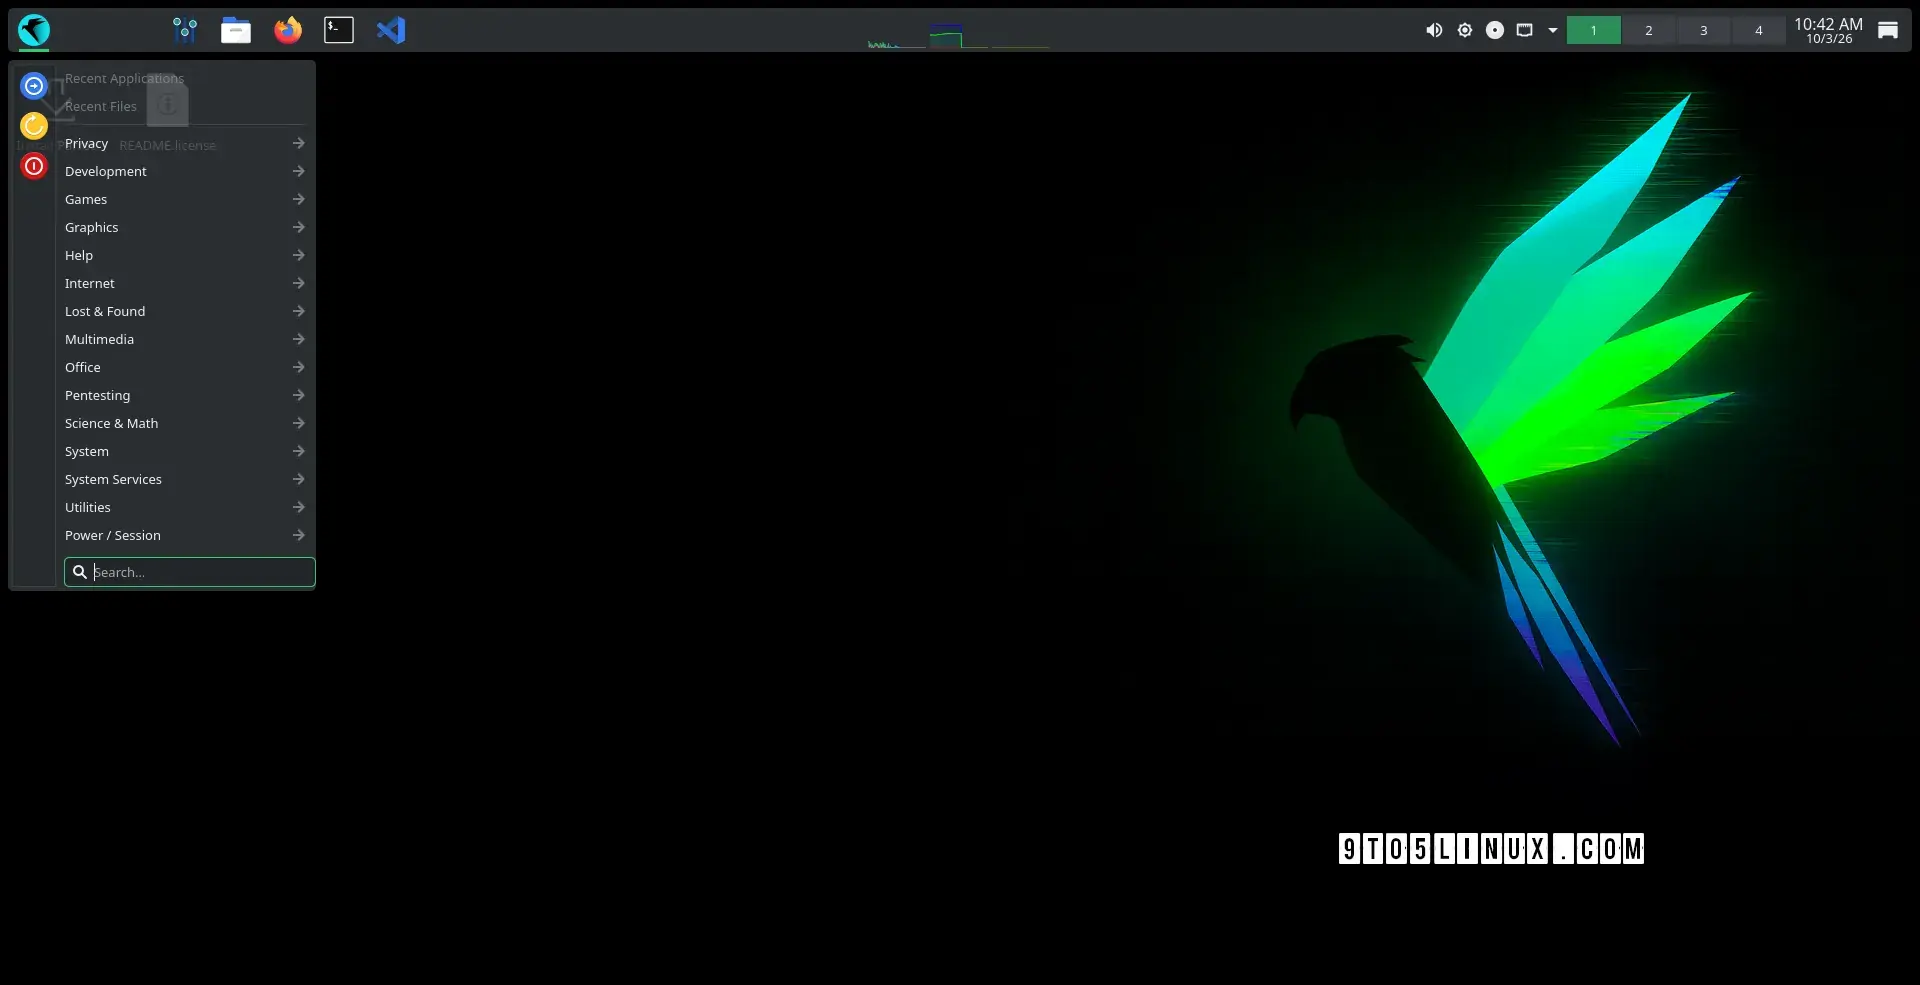
#Debian-Based Parrot OS 7.4 Released with AnonSurf 6.0, Updated #RaspberryPi Images, and #Linux Kernel 7.1 https://9to5linux.com/parrot-os-7-4-released-with-anonsurf-6-0-updated-raspberry-pi-images
@parrotsec #security #infosec #OpenSource
Alt...
A screenshot of Parrot OS 7.4 with the KDE Plasma desktop environment showing the application menu.
Latest #Debian 13 “Trixie”#Linux Kernel #Security Update Patches More Than 1300 CVEs https://9to5linux.com/latest-debian-13-trixie-kernel-security-update-patches-more-than-1300-cves
Alt...
Debian 13 splash screen
#Hacks of 2 federal agencies in a month have spilled a bonanza of sensitive data
The #Pentagon is informing more than 2 million current & former military members that their personnel records storing sensitive personal info were stolen over a months long compromise of one of its networks. The #breach is the second one in recent months to expose sensitive gov information.
The records, according to one notification letter posted to Reddit, included #SocialSecurity numbers, names, addresses, sex, race, & occupational specialty. This last category could be particularly valuable to foreign adversaries because it could help their intelligence agencies in identifying high-value #military personnel. Starting last October, #hackers gained access to a system operated by the #DefenseManpowerDataCenter , which collates Dept of #Defense personnel records. The Pentagon says that the breach compromised the records of 2.8 million living individuals.
#privacy #security #dod

ansible-jailexec 2.0.3 is out: a security release for the Ansible connection plugin that runs tasks inside FreeBSD jails via jexec.
Files pushed into a jail were staged in /tmp on the jail host with the source file's mode (often 0644), so other local users on the host could read them during the transfer. Staging now uses a private 0700 directory.
Thanks to GitHub: manus-pi for the report!
Advisory: https://github.com/chofstede/ansible_jailexec/security/advisories/GHSA-cfm5-946c-m3qx

"Adversarial distillation poses safety and national security risks."
Okay, so when US AI companies use tonnes of data in violation of the license, it's fine. But when anyone else does it, it's a national security risk.
"Extracted reasoning could be used to train another model without preserving the safeguards applied to the original model's user-facing outputs."
Right, because US AI companies have demonstrated such careful consideration for safety, responsibility and ethics thus far. It's not like they've only very recently failed to follow basic security principles in sandboxing and suffered zero consequences as a result or anything like that.
Irony alert: OpenAI whines that Chinese model stole its special IP that it stole from everybody else
https://www.theregister.com/security/2026/09/30/irony-alert-openai-whines-that-chinese-model-stole-its-special-ip-that-it-stole-from-everybody-else/5300285 #news #security
NVIDIA security bulletin for Sept 30 notes many GPU issues https://www.gamingonlinux.com/2026/09/nvidia-security-bulletin-for-sept-30-notes-many-gpu-issues/


I'm starting to see signs other people are slowly coming the realization that AI companies have more enshittification cards in their hand.
I attended an Anthropic training hosted by Anthropic employees. During the presentation, on almost every slide, the trainer reiterated "If you're experiencing issues with the quality or correctness of the output, you can solve that by giving Claude more access to your internal documentation and intellectual property." Almost every answer to every question included "and make sure you give Claude full access to your files and identity so it see everything you see and act as you." As a nearly 30yr veteran of infosec, I assumed this was an advanced adversary attempting to exploit us. 😂
The AI companies _WILL_ eventually operate solely by extracting value from all their customers and business relationships for their shareholders. We already know what this looks like. Anyone bought an Amazon Basics product? Amazon tracks products that do well, they then rip off the design of those products and launch a cheaper version under the Amazon Basics brand.
"But, Brad, AI companies are more ethical than.. no wait, I heard it." Right, so, let's say you're Cursor. You announce a profit for the first time in your history. What happens next? OpenAI raises your rates to nullify your entire profit. This happened, in real life.
You're a math researcher working on a research problem with a prize using OpenAI for assistance. What happens next? OpenAI rips off all your work and uses it to train an expert model to solve the problem and win the prize. This happened.
Wake up, sheeple! 😂 If you have a good idea and use _any_ thirdparty AI service to create it, you are handing your work over to the AI companies and your competitors.
Legal precedent is AI generated code is not IP because a human didn't create it. But every line of code Claude or Codex generates for your proprietary application is stored on their servers for as long as they afford to save it.
As these companies pivot to IPO and beyond, just take a moment to consider the history of Silicon Valley and what their next steps are for further monetizing the data they're collecting on you.
German #police read #Signal, #Telegram, #WhatsApp messages without breaking encryption
Apps such as WhatsApp Web and Signal Desktop allow people to use their accounts on other devices, such as laptops or desktops
Germany’s Customs Office has been using these features to connect a police-controlled computer to a suspect’s account.
Once connected, messages can be delivered to that computer without the police having to crack the encryption protecting them.
https://cybernews.com/privacy/police-telegram-whatsapp-signal-surveillance-linked-devices/ #security #privacy
OpenBSD 8.0 is due out soon, and -current snapshots identify as 8.0 already. So it's time to reprise "You Have Installed OpenBSD. Now For The Daily Tasks." https://nxdomain.no/~peter/openbsd_installed_now_for_the_daily_tasks.html which should help answer some common questions. #openbsd #newrelease #maintenance #sysadmin #security #dailytasks #freesoftware #libresoftware

#Debian [DSA 6528-1] linux kernel #security update has fixes to 1313 CVEs.
https://lists.debian.org/debian-security-announce/2026/msg00441.html
Software-Problem verzögert Zulassung neuer Boeing-Variante
Boeing hoffte auf die Zulassung für die größte Variante des wichtigen Modells 737. Doch ein neuer Software-Fehler bringt den Zeitplan erneut durcheinander.
#Automatisierung #Luftfahrt #Security #Technik #Wettbewerb #Wirtschaft #news
Australian push for an import ban on 'pervert' smart glasses
#tech #technology #news #technews #security #privacy #smartglasses #pervertglasses