Search results for tag #linux

Hello again, fediverse! 👋
I’m Alex, a Linux sysadmin in Scotland 🏴. I first joined in 2019, then wandered between servers and took a few breaks along the way, so consider this a fresh start.
I’m now running my own instance on GoToSocial, because I enjoy self-hosting things I probably don’t need to self-host. Outside of work I dabble in music production and plan to start on game development, both strictly as hobbies. Expect a mix of homelab tinkering, Linux war stories, open-source and privacy chat, the odd travel photo, and whatever I’m playing or listening to at the moment. I’ll use content warnings for heavier topics and alt text on images.
Question for you: what’s the best thing you’ve self-hosted that you couldn’t live without now?
#introduction #Scotland #SelfHosting #GoToSocial #Linux #SysAdmin #OpenSource #Privacy #MusicProduction #GameDev

🚀 Franchement, Remark42 sur Wiki.js 3, c'est un régal !
Zéro pistage, une intégration aux petits oignons avec le thème du wiki et le support complet du Markdown pour poster de beaux commentaires (code, images, citations… tout passe ✨).
Je ne regrette vraiment pas ce choix ! Découvrez le tuto complet et venez tester ça dans les commentaires 👇
👉 https://wiki.blablalinux.be/fr/deployer-remark42-docker-nginx-proxy-manager-wikijs-3
#Linux #LogicielLibre #AutoHebergement #Wikijs #Remark42

pvetui v1.4.5 is out!
Highlights:
• Added Windows portable manifests, split VM/LXC counts, and fixed SSH agent handshake.
Full notes: https://github.com/devnullvoid/pvetui/releases/tag/v1.4.5 #proxmox #linux #homelab

Ich hatte eine rege Diskussion mit Microsoft Deutschland vor Ort an meinem Arbeitsplatz.
Man wollte mir erklären, dass #Opensource skaliere. Ich habe so hart mit Ihm und seiner Kollegin diskutiert, mit einer ausführlichen Erklärung, dass er lüge und keine Ahnung hätte.
Dies führte vor 3 Wochen sogar zu einem Raunen in dem Raum seitens der Kollegen:innen der Standorte, welche vor Ort waren.
Ich sehe, wie es skaliert.
Lieblingssatz im Artikel von @heiseonline :
Microsoft sucht nach neuen Ansätzen, da „unsere Maßnahmen bislang nicht die erwartete Entspannung gebracht haben.“ Wie sich herausstellt, wird ein Kernprozss der Server überlastet, was zu deren Absturz und unzulänglichen Cloud-Kapazitäten führt…

Oops!

Alt...
Screenshot of a post on X by Tom Siwik (@tomhacks) with a verified blue checkmark, posted at 4:01 PM on Nov 11, 2026, showing 277.4K views. The post reads: "Omarchy folks. Less slop, more code reviews, please v3 -> v4 migration just deleted my network setup without warning. SSH gone, tailscale gone. And migration never finished bc of a browser bug. That's not called a migration"
🐧 Parlez-vous couramment le jargon Linux et auto-hébergement ?
Pour éviter les maux de tête devant des acronymes comme LXC, OAuth ou JWT, le Wiki BlablaLinux accueille désormais son propre glossaire ! 🎉
Survolez les termes techniques dans les articles pour comprendre instantanément de quoi on parle, sans même quitter votre lecture 👇
#Linux #AutoHebergement #LogicielLibre #OpenSource #Wikijs


Connecter son Wiki.js v3 avec GitHub sans se prendre la tête avec le reverse proxy ? C'est par ici 👇
https://wiki.blablalinux.be/fr/activer-authentification-github-wikijs-v3


After months with the good old cwm, I'm giving bspwm a try. I love configuring my desktop with shell scripts, and tiling is a nice bonus.
My workflow stays simple:
I: Firefox
II: xterm + tmux
III: IRC
Also enjoying the tiny sxbar!
Light enough for my ThinkPad T60 and X220, yet running on my T14 (i7, 40GB RAM).
Don't worry, those 40GB get some exercise when compiling SlackBuilds and Linux kernels.
And don't be fooled by the minimalist desktop... Firefox alone is eating 1.5GB of RAM! 😂


I've always appreciated the simplicity of the BSDs. Power, yes, but without unnecessary complexity.
BastilleBSD and vm-bhyve have been my trusted companions for many years. But whenever I used Linux, I missed them.
That's why, years ago, I started putting together a collection of shell scripts (and some Python, although to a much lesser extent) to create something somewhere in between.
A bit of Bastille, a bit of vm-bhyve, a bit of Proxmox: unprivileged Linux system containers and virtual machines, managed from the command line.
Live backups. And live restore: bringing a workload back online before all its data has finished copying from the backup. Multiple storage backends. Encryption at the storage or individual workload level. Different networks. Isolation of each workload (a bit like illumos zones), with additional layers of protection.
Each container has its own UID/GID mapping. VMs run under separate unprivileged identities, with namespaces, seccomp and resource limits adding further layers of protection.
Pull-based backups from external hosts, with different levels and types of encryption. With raw encrypted ZFS replication, the backup server doesn’t even need the decryption keys. Backups are pulled over SSH by an external server. The workload host holds no credentials to log in to that server.
It also runs on a 1 GB Orange Pi PC 2, where I’ve tested both containers and native ARM64 KVM guests. And on a Orange PI One, armv7 and 512MB, it can run some lxc containers without problems, from the SD, using f2fs.
Simple disaster recovery. Because after those 142 servers went up in flames in Strasbourg, disaster recovery became something I care a lot about.
Currently supported and tested on Alpine Linux, Debian 13 and Armbian. On Debian, LXC containers also run under enforcing AppArmor profiles, adding another layer of protection.
Few commands. Lots of power. And it's called "Jail It!"
I'm not going to release it, at least not for now. I need to focus on my other projects, and Jail It! still needs some cleaning up.
But it works. And it does its job very well.
For containers, there's absolutely nothing running in the background. For VMs, just a small Python helper. No continuously running services. You connect via SSH, run your commands, and that's it.
Still, for anyone curious enough to have a look, I've put together a short demo on Asciinema:
https://asciinema.org/a/BbwGs99U9UJDLAzZ
Well, "short" might be a bit of an exaggeration. It's quite long, but I think it's worth watching all the way to the end.
#Linux #LXC #KVM #FreeBSD #Virtualization #OwnYourData #BSD #SelfHosting #Homelab #SysAdmin #DisasterRecovery
🐧 Nouveauté sur le Wiki BlablaLinux !
Un tuto qui coince ? Une commande à améliorer ? Juste envie de dire merci ?
Les commentaires sont maintenant ouverts sous tous les articles grâce à Remark42 🚀
Et comme on partage tout ici, je vous ai même préparé la doc pas-à-pas pour l'installer sur votre serveur :
👉 https://wiki.blablalinux.be/fr/deployer-remark42-docker-nginx-proxy-manager-wikijs-3
Testez ça en bas de la page ! 💬
#Linux #AutoHebergement #LogicielLibre #Remark42 #SelfHosted

Zu den #CLT2027 möchten wir mit euch zum Thema "Selber denken lassen" in den Austausch kommen. Was lassen wir von Maschinen erledigen, wo denken wir noch selbst und welche Entscheidungen überlassen wir anderen?
Beitragseinreichungen sind ab sofort bis zum 04.01.2027 möglich:
➡️ https://chemnitzer.linux-tage.de/2027/de/presse/mitteilungen/pm01
➡️ Call for Lectures: https://chemnitzer.linux-tage.de/2027/de/programm/call-for-lectures
➡️ Call for Presentations: https://chemnitzer.linux-tage.de/2027/de/programm/anmeldung/live
#linux #tux #chemnitz #ChemnitzerLinuxTage
Alt...
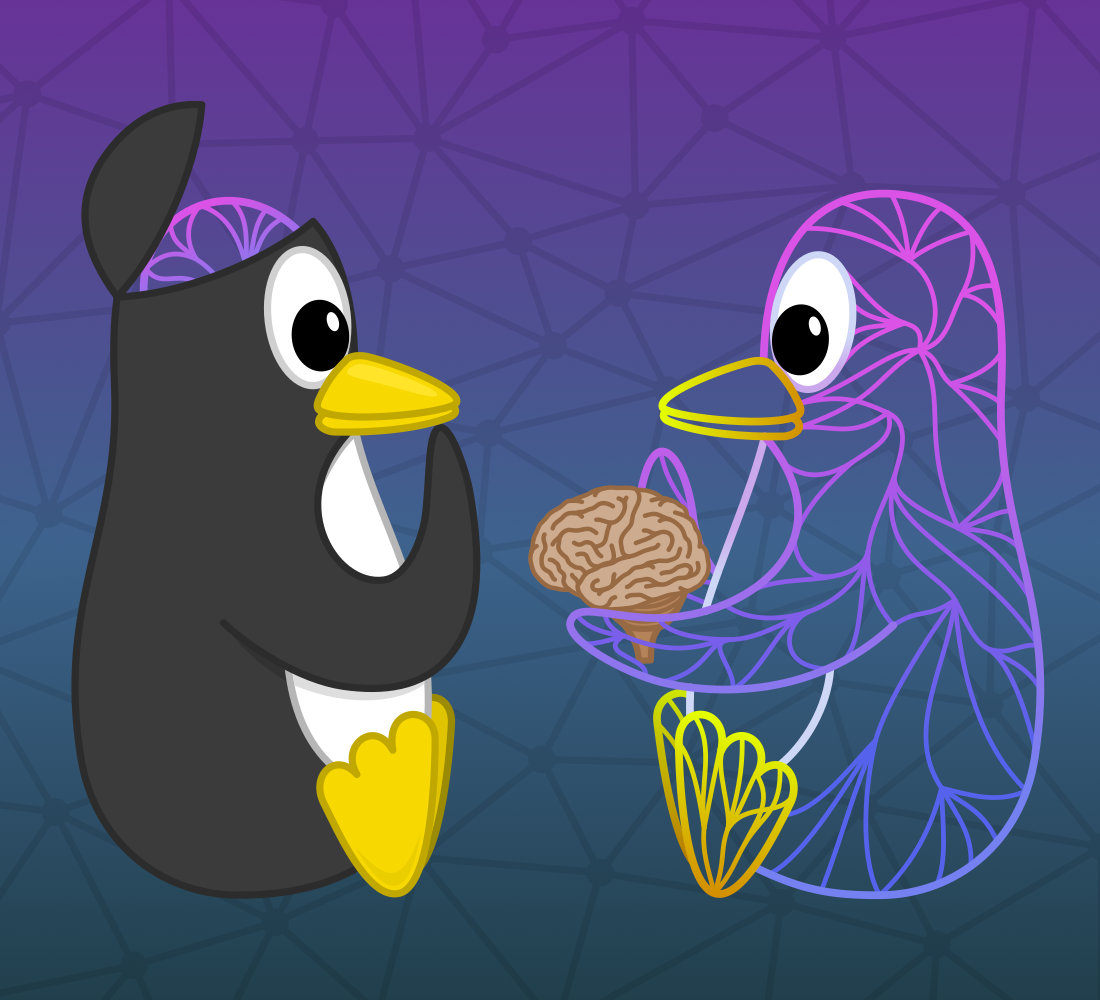
Zwei gezeichnete Pinguine sitzen sich gegenüber und schauen sich gegenseitig in Denkerpose an.
Der linke Pinguin ist ein "lebendiger" Tux mit einem "künstlichen" Gehirn; der rechte Pinguin ist ein "künstlicher"/technisierter Tux, mit einem "natürlichen" Gehirn auf einem seiner Flügel.
I really, really reeaaallly want to see #Sylve becoming a FreeBSD based replacement or alternative to #Linux solutions like #XCPng (#Xen) or #Proxmox (#KVM).
Also interesting for my own @BoxyBSD@bsd.cafe project utilizing this feature. So, I've been working at this for some time now.
First working draft moving a VM which has its storage on a NFS server (ZFS based send/rec. as local storage to follow), including multi CPU support. But there's a catch - I'm not sure if I want to publish this later under MIT, rather than GPLv3 or AGPLv3, so this could be a problem for upstreaming.

Alt...
bhyve VM live migration on FreeBSD 15
Für alle, die vielleicht gerade erst mit #Linux loslegen: Traut euch an die Kommandozeile, es lohnt sich. Hier sind ein paar erste Befehle zum Loslegen. Vielleicht ist ja auch für Fortgeschrittene noch der eine oder andere Parameter dabei, der unbekannt ist.
New Guide: Where to follow more Linux news without the clickbait https://www.gamingonlinux.com/guides/view/where-to-follow-more-linux-news-without-the-clickbait/


🤖 Et si vous pouviez interroger votre wiki en langage naturel depuis votre terminal ?
Wiki.js 3 intègre un serveur MCP. Mon nouveau guide explique comment le connecter à Gemini CLI et OpenCode : jeton d'accès, réglages Nginx Proxy Manager pour le streaming, et astuces pour éviter les blocages de quota.
📖 https://wiki.blablalinux.be/fr/piloter-wiki-js-3-gemini-cli-opencode-mcp
#WikiJs #MCP #GeminiCLI #OpenCode #SelfHosting #Linux #LogicielLibre #BlablaLinux

@marocddot How can you miss it? It is still there. I believe it is in all distros of #linux and all #bsd's by default.


@pertho @raster i'm a linux gal vehemently opposed to the scourge of penguin slopification, who has no #bsd skills yet, & hence whose initial attempts to install #OpenBSD in a #qemu VM for learning & evaluation, have so far failed [base cli system done ok, but both attempts then for MATE failed]. My potential interest in also testing #FreeBSD so far has been arrested by my concern wrt their ai attitude, which now seems to be solidifying in the wrong direction, so i doubt i shall bother even trying it now, alas.
#DropbearPooterising #Linux #LinuxWomen #FOSS
#FuckGenerativeAI #FuckSlopbots #AntiAI #NoAI
service: our devices are too hard to install
me: our devices aren't too hard to install, they are #embedded #linux devices installed on customer networks, in #IT environments we cannot control, requiring ad-hoc and typically bespoke configuration
#service: well you should make a configurator
me: we totes can, itll take 15 staff months of work or $xxxxxx.
service: #productmanagement doesn't want to spend that
me: as is their perogative. So if we can't make our product better (for you guys) we have to better equip your guys to deal with the product as is. I can whip up a course, or recommend some online courses.
service: we don't have time for that.
me: ok, then your alternative is stop hiring your guys from traditional industries, thinking you can train #networking skills and start hiring your guys from IT backgrounds and train them on our customer industries
service: welcome to the new service guy he has 20 yrs of aerospace experience
me: I fucking give up.

The #KDE development team announced today it has learned that a third-party animated wallpaper plugin for KDE #Plasma called NeoNova, is a piece of malware that could infect #Linux computers running the Plasma desktop environment. Read more: https://www.newinlinux.com/kde-wallpaper-plugin-neonova-is-malware/
#Malware #Security
my memory of drawterm is fading 4
#unix_surrealism #openbsd #netbsd #plan9 #9front #glenda #unix #comic #linux
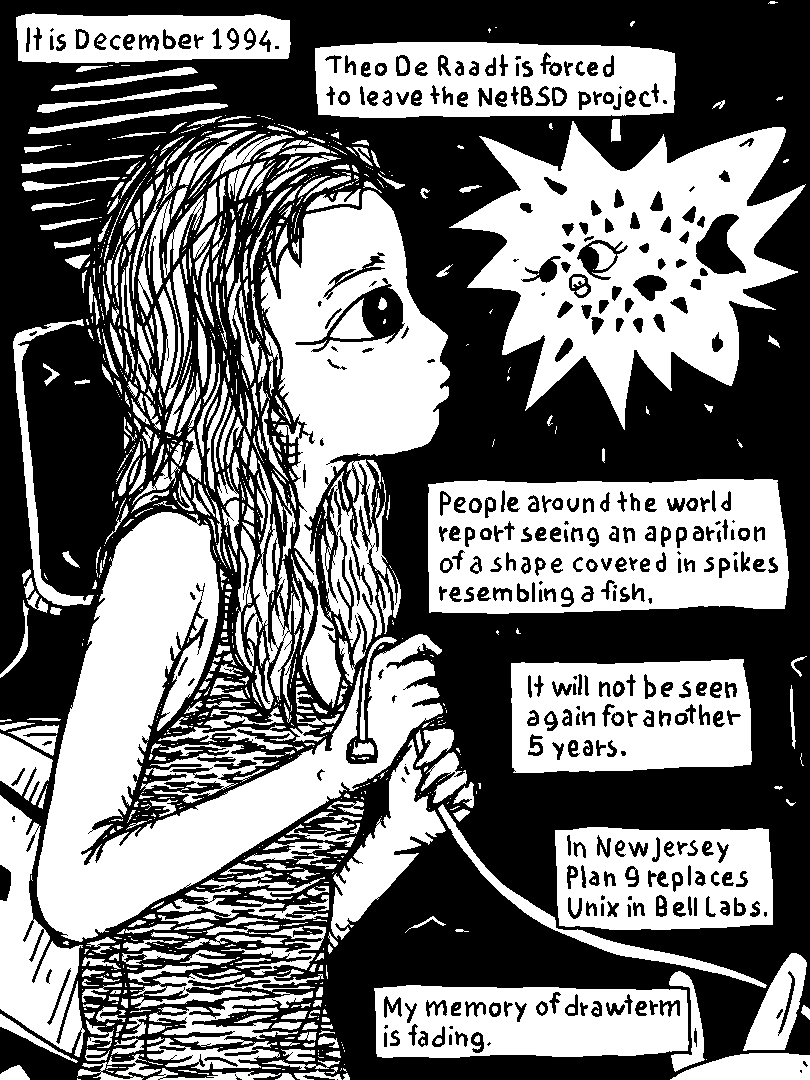
Alt...
It is december 1994.
theo de raadt is forced to leave the netbsd project.
people around the world report seeing an apparation of a shape covered in spikes resembling a fish.
it will not be seen again for another 5 years.
in new jersey plan 9 replaces unix in bell labs.
my memory of drawterm is fading.

ALRIGHT! I'm VERY excited to announce this research, because we've been holding onto it for close to a year now!
Announcing File Notification Attacks! Side-Channel Leakage from the File-Notification System on #Linux, #Android, #Windows, and #macOS
We've found decades-old bugs on Linux, Android, and Windows... well technically Microsoft considers what we found an ✨ undocumented feature ✨ (got Microsoft nominated for the lamest vendor response #pwnie award haha).
There's SO much to talk about, so please expand this thread below, but you can also check it out yourself at:
There's a #noAI logo that my sister drew there. Our work was accepted at #CCS 2026, and I'll be presenting it this November at The Hague, Netherlands! If you're there, we should totally meet up :D
Thanks to my AWESOME co-authors: Xufan Zhao, Jeanette Angelika Wultsch, @hweissi, Florian Draschbacher, @notbobbytables, and @lavados 🙏, all of us from @isec_tugraz, TU Graz

Torchlight II: Steam login replaces TapTap.io for online multiplayer
https://playingtux.com/en/articles/2026/11/torchlight-ii-steam-login-replaces-taptapio-released/
#Linux #Gaming #LinuxGaming #Torchlight2 #ActionRPG #HackAndSlash #Steam


"Linux kernel reviewer steps down from memory management duties due to influx of AI slop patches"
"Linux kernel memory-management code reviewer steps down due to influx of AI slop patches — volume of submissions coupled with low manpower forces the step back"
A critical flaw present in every operating system since 1971 allows anyone who opens a terminal to obtain a fully interactive shell. Instantly. With no authentication beyond the one they already did.
Terminal2Shell is a design-level vulnerability in terminal emulators. When a terminal is launched, it immediately spawns a shell process and connects it directly to the user's keyboard. From there, the attacker can issue arbitrary commands with the full privileges of the logged-in user.
#Terminal2Shell #Unix #Linux #MacOS #Windows #Security #FOSS #FreeSoftware
What if any process could handle SIGKILL?
An interesting question, and a detailed technical rundown of how to make this happen, which involved building a custom Linux kernel, of course.
I really, really enjoy the conclusion.
And you know? It turned out fine. Nothing exploded on my system. As I could predict, because this was otherwise impossible, nobody did it. The signal system was setup i
https://www.osnews.com/story/146346/what-if-any-process-could-handle-sigkill/
Une nouvelle tuile vient de faire son entrée sur le portail web ! 🚀
Je viens d'ajouter ByteStash à l'annuaire des services. Un super outil auto-hébergé pour stocker et partager rapidement des extraits de code et des notes.
👉 À retrouver dès maintenant sur https://link.blablalinux.be
Over the past few days, I've been working on some Linux-based setups, bringing back some of my old solutions (with a few adaptations) to make them work the way I like. Mostly inspired by some of the ideas of simplicity that come from the BSD world.
I'm using Alpine Linux as a base, and I've been testing these setups on both proper servers and SBCs, for various reasons.
And, all things considered, some distributions (like Alpine, for example) have remained fairly true to the original ideas of simplicity and predictability. I still enjoy using Linux when it’s logical and predictable.
And this got me thinking: some distributions have gone from:
"Hey, we're a solid, simple, and reliable alternative to Windows. Give us a try!"
to:
"Hey, we support practically all your hardware, just like Windows" (which, to be fair, was a real achievement)
to:
"Hey, Windows! I’ve become just like you!"
As if complexity automatically meant "enterprise-grade", and being "enterprise-grade" were something everyone should aspire to - even on a laptop or a small SBC.
There's nothing wrong with solving complex problems. Some complexity is unavoidable, and sometimes even necessary. But complexity should be the price we sometimes have to pay to solve problems, not something we proudly advertise as a feature.
Otherwise, we end up exactly where we started: just like Windows. Or perhaps even worse.

RE: https://social.vivaldi.net/@Vivaldi/117593812717631891
Unfortunately, day 2 of Web Summit has been cancelled due to weather. I had so looked forward to this talk, but not this time. However, I have two more talks on Thursday and I hope those of you at Web Summit will attend those instead. We are also having a press conference Thursday, so we’re staying busy. And you should stay tuned.
#Vivaldi #WebSummit #Browser #Windows #Macos #Linux #AI #Technology #EU #Europa


This New #Linux-Based #Desktop #OperatingSystem Is Built for #AI Nerds
Hailing from #Cyanogen’s cofounder, #Kora is alternative to Windows and macOS for power users running #localAI
Targeted to creators and developers, Kora’s central idea is to bring AI together at system level and help power users interact more seamlessly with multiple providers, rather than siloing everything into desktop apps and browsers. It’s scheduled to launch in 2027.
https://www.wired.com/story/kora-new-linux-based-desktop-operating-system-is-built-for-ai-nerds/
https://archive.is/20261110144156/https://www.wired.com/story/kora-new-linux-based-desktop-operating-system-is-built-for-ai-nerds/
3/3
Hashtags: #KuketzForum #Forum #MikeKuketz #Mike #Kuketz #IT #Sicherheit #Datenschutz #hacking #Auswahl #Beiträge #Themen #Distribution #Distro #Manjaro #Linux #sichermachen #absichern #härten #Hacktivismus #Aktivismus #Hacker #hacken #legal #illegal #Bewertung #Einschätzung #Justiz #juristisch #Gesetze #Sichtweise
Asahi Linux ändert Lizenz: Mit Copyleft gegen Code-Übernahme durch Forks
Asahi Linux stellt seinen Code unter Copyleft und begründet das mit Projekten, die seine Arbeit ohne Herkunftsangabe übernehmen. Namen nennt Asahi nicht.
Linux Mint 27 Adrien: primeras pruebas con Cinnamon, Wayland y el nuevo kernel 7.3.3 #distros #btrfs #cinnamon_6.8 #distribuciones_linux #flatpak #kernel_linux_7.3.3 #linux #linux_mint_27 #linux_mint_27_alpha #linux_mint_adrien #linux_para_principiantes #proxmox #software_libre #ubuntu_26.04 #wayland #xfs
https://soploslinux.com/linux-mint-27-adrien-primeras-pruebas-con-cinnamon-wayland-y-el-nuevo-kernel-7-3-3/

Du hast dein Weiterbildungsbudget 2026 noch nicht ausgeschöpft?
In unseren Linux-Schulungen sind bis Jahresende noch ein paar Plätze frei. Ob #Linux-Administration, Virtualisierung mit #Proxmox, #Ansible, Container und #Kubernetes, Monitoring mit #Checkmk oder der sichere Betrieb von Mailservern: Unsere Kurse vermitteln Wissen, das du im Admin-Alltag direkt anwenden kannst.
Starte mit unseren Schulungen gut vorbereitet in dein Linux-Jahr 2027!
Jetzt Kursplatz sichern:
https://www.heinlein-support.de/news/freie-plaetze-linux-schulungen-2026-heinlein-akademie
Alt...
Foto Kursteilnehmender

@fsfe I really appreciate the FSFEs work over the decades but the focus on proprietary mobile platforms while there are #FreeSoftware alternatives with openess and user freedom built in strikes me as odd.
Let's rather make sure those Free Software Android apps continue to run great on #MobileLinux (we don't need anything from google for that) and put the money into moving a platform forward that has freedom and openess built in from the ground up.